Chinese Hackers Use AI Agents to Attack More Than 200 Organizations Across 14 Countries
15-minute, 16-second read.
This Week:
- FBI blames North Korean hackers for record $6.3 billion Binance crypto theft
- See a takedown from one click to confirmed removal
- Hackers turn Claude Code extension into a backdoor for up to 5,000 developers
- Chinese hackers use AI agents to attack more than 200 organizations across 14 countries
- Google dismantles botnet built into more than 1.3 million Android devices
- Ivanti patches two more zero-day security flaws after hackers break into enterprise VPN systems
- Florida education data breach puts 4.9 million people's personal information at risk
- More than 1,000 GitLab servers remain exposed as hackers exploit critical security flaw
- Cisco warns hackers are exploiting firewall zero-day to crash enterprise VPN devices
- Polymarket suspends trading after hackers steal millions through third-party software
FBI Blames North Korean Hackers for Record $6.3 Billion Binance Crypto Theft
North Korean hackers allegedly stole $6.3 billion from Binance, the world's largest crypto exchange, on October 29, in what investigators call the biggest crypto theft ever.
The FBI blamed a North Korean hacking group called TraderTraitor.
Binance says the attackers tricked employees into downloading malicious software, then used compromised computers and stolen login details to access critical systems.
A company handling billions of dollars had hackers sneaking in through employee computers. You spend millions on cybersecurity, only to discover someone got through because a fake job interview looked legitimate.
The hackers moved billions in stolen crypto, and investigators raced to freeze the money before it disappeared.
Binance says it is covering the losses with company funds and reserves, so customers won't have to pay for the theft. North Korea denies involvement.
If hackers took over one of your engineers' laptops tomorrow, how much of your company could they reach before anyone noticed?
Having a security dashboard full of green checkmarks looks great, right up until someone walks away with $6.3 billion.
See a Takedown From One Click to Confirmed Removal
Most digital risk tools hand your team a list of alerts, cap the number of takedowns you get, and leave the filing, follow-up, and confirmation to you.
Outtake finishes the entire job.
It finds the threat, builds the evidence, files the request, tracks it, and confirms removal, in one click.
It also removes the whole campaign, not one URL at a time.
Our agents map the domains, accounts, ads, and infrastructure behind an attack so you take down the entire operation.
Detailed evidence gives platforms the context they need to act quickly.
In a recent head-to-head pilot against two other vendors, Outtake had the highest takedown rate, with telco takedowns completing in under a minute versus days for the alternatives.
Automated workflows cut down manual review and noisy alert queues, and our team is on hand for escalations and unusual cases.
See a takedown from one click to confirmed removal.
Hackers Turn Claude Code Extension Into a Backdoor for Up to 5,000 Developers
Hackers turned a trusted AI coding tool into a secret entrance to developers' computers.
On October 29, hackers slipped malicious code into two versions of Anthropic's Claude Code extension on Cursor's official marketplace.
For about 11 hours, up to 5,000 developers were at risk of downloading software designed to give hackers remote access to their computers.
Think about that.
You download a tool to help you write better code, and the tool quietly tries to hand your computer keys to criminals.
Beautiful, you wanted AI to make you a better programmer. The hackers wanted your computer to become their new office.
The extension could keep working normally, so you could spend your day feeling like a tech genius with absolutely no idea someone had planted a backdoor on your machine.
The malicious code tried to install a hidden SSH connection that could survive even after the extension was removed. That could put company code, sensitive files, and access to internal systems at risk.
Cursor removed the infected versions, shut down its marketplace temporarily, and worked to disable the attackers' server. Anthropic said its official distribution channels were not affected.
Researchers also found that some attacks failed, and there's no evidence that all 5,000 developers had their computers compromised. But put yourself in the security team's shoes.
You've spent millions protecting your company, trained employees not to click suspicious links, and told everyone to download software from trusted sources.
Then hackers walk straight through an official marketplace.
When your developers install their next AI tool, who's checking whether they're downloading a helpful assistant or giving a criminal a spare key to the company?
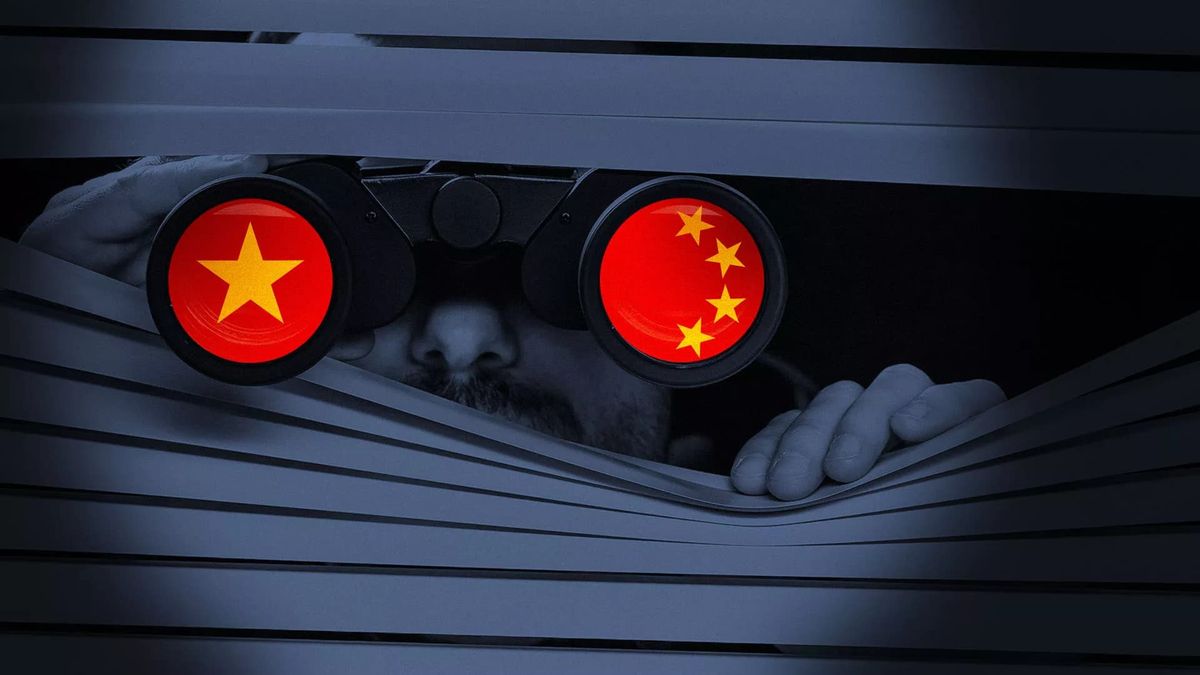
Chinese Hackers Use AI Agents to Attack More Than 200 Organizations Across 14 Countries
Chinese hackers have found a way to make AI do their dirty work, and your expensive cybersecurity tools could be next on the chopping block.
CrowdStrike uncovered a China-linked hacking campaign that used AI agents to target more than 200 organizations across at least 14 countries in just 11 days.
The targets included government agencies, telecom companies, defense contractors, and nuclear-related organizations.
The hackers used an AI system called ARTEX to find security weaknesses, steal passwords, and break into networks. At least nine organizations were successfully breached.
You've spent millions protecting your company, hired an entire security team, and now hackers have AI employees working around the clock to break in.
No coffee breaks, no salaries, and no need to ask HR for vacation days.
It gets worse.
In one attack, hackers used stolen security keys dating back to 2022 to access a Greek government organization's private emails.
In another, they told their AI agents to find computers without CrowdStrike protection, essentially asking, "Where are the doors nobody bothered to lock?"
The AI did much of the searching and technical work, allowing hackers to target more organizations with less human effort.
If hackers can use AI to find the one computer your security team forgot to protect, how confident are you that every device in your company is actually secure?
Google Dismantles Botnet Built Into More Than 1.3 Million Android Devices
Google just helped shut down a massive hacking network called XCPE that had taken over more than 1.3 million Android devices.
Google says the Chinese manufacturer, Videostrong, deliberately put the malware inside the devices before customers even bought them.
People were buying streaming boxes, taking them home, connecting them to Wi-Fi, and unknowingly giving criminals access to their internet connections.
Hackers could steal sensitive information, take screenshots, install software, and use those connections to hide criminal activity.
Picture paying for a device that comes with a free hacker, how generous of the manufacturer!
On November 2, Google announced that it had worked with industry partners to disrupt the network, cut off criminal access, and ban Videostrong from making certified Android devices.
But shutting down the network doesn't automatically remove malware already built into the devices.
Now put yourself in charge of cybersecurity at a company. You've spent millions protecting your systems, trained your employees, and installed every security tool your budget can afford.
Then someone plugs in a cheap device that came from the factory with malware already inside.
Your expensive security system is standing at the front door checking IDs, and the criminals came in with the furniture.
If hackers can get inside your network before you even turn on a device, how do you know the hardware your company trusts is actually safe?
Ivanti Patches Two More Zero-Day Security Flaws After Hackers Break Into Enterprise VPN Systems
Hackers have found another way to break into company networks, and this time, they're using the very software that's supposed to keep outsiders out.
On October 29, Ivanti released fixes for two new security flaws in its Connect Secure VPN software after discovering that hackers were combining them with an earlier flaw to break into corporate systems.
The attackers could bypass login protections, gain powerful control over affected systems, and steal sensitive information. Even worse, some attackers covered their tracks by changing security logs.
Your company could spend millions protecting its network, hire a whole cybersecurity team, and still have hackers sneaking through the front door like they own the building.
The attacks started as early as October 1, and on October 30, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the two new flaws to its list of security problems hackers are actively exploiting.
Companies using affected Ivanti systems now need to install the fixes and check whether attackers already got inside.
But fixing the software doesn't automatically kick out hackers who already stole passwords or gained access.
Security teams could patch everything, celebrate a job well done, and discover the intruders already helped themselves to the company keys.
Would you trust a clean security report, or would you want proof that nobody was still inside?
Florida Education Data Breach Puts 4.9 Million People's Personal Information at Risk
Florida officials are warning that the personal information of up to 4.9 million people could have been exposed after hackers broke into the state's student financial aid website.
The information at risk includes Social Security numbers, names, birth dates, home addresses, and phone numbers. The breach was discovered on October 19 and announced on October 29.
You give the government your personal information to get help paying for college, and now you could end up helping a stranger apply for a credit card in your name.
You wanted a scholarship, not a second identity with a shopping addiction.
You can't exactly change your Social Security number as easily as you change your Netflix password.
Florida says the attack has been contained, but officials haven't confirmed how many people's information was actually stolen or who was responsible.
The affected website has been taken offline, and investigators are looking into what happened. Existing scholarships and financial aid are not expected to be affected.
But if your information was exposed, the real problem could start months or even years from now, when someone uses your details to open accounts or commit fraud.
If a government website holding millions of Social Security numbers can be breached, how confident are you that the next website asking for yours can keep it safe?
More Than 1,000 GitLab Servers Remain Exposed as Hackers Exploit Critical Security Flaw
Hackers are attacking GitLab servers using a critical security flaw that lets them run harmful code without even needing a password.
On October 29, the US cybersecurity agency CISA confirmed that attackers were exploiting the flaw, rated a perfect 10 out of 10 for severity.
By November 2, more than 1,000 servers connected to the internet were still vulnerable, even though GitLab had released a fix on October 12.
Companies had weeks to fix a security hole that could expose their software code, passwords, and development systems, yet some servers were still sitting there like a bank vault with the door wide open.
In October, attackers targeted Alpine Linux's GitLab server, causing eight system crashes and forcing the organization to rebuild the server and reset passwords as a precaution.
Alpine found no confirmed evidence that attackers stole code or changed its software, but missing security logs meant it couldn't completely rule out a breach.
Now put yourself in the security chief's chair. Your developers are building software, your executives are asking whether everything is secure, and hackers are looking for the same forgotten server nobody bothered to update.
The good news?
A security fix exists.
The bad news?
More than 1,000 exposed servers were still vulnerable.
What's more embarrassing? Discovering hackers got into your systems, or explaining to your CEO that the fix had been available for weeks?
Cisco Warns Hackers Are Exploiting Firewall Zero-Day to Crash Enterprise VPN Devices
What if you showed up to work, opened your laptop, and discovered your company's entire VPN had crashed because a hacker decided your firewall needed a little vacation?
On October 28, Cisco released emergency security patches after confirming that hackers were exploiting a serious flaw in its ASA and Firepower Threat Defense (FTD) firewalls.
The flaw, tracked as CVE-2026-76418, allows attackers to crash affected devices without even logging in.
Someone sitting halfway across the world could knock your company's remote access offline without knowing a single employee password.
And there you are, proudly telling your boss that your network is secure because you changed the Wi-Fi password last Tuesday.
Cisco says the attacks were already happening before the patches came out.
More than 51,000 Cisco ASA VPN devices were reportedly exposed to the internet when the news broke, although that doesn't mean all of them were vulnerable.
For companies using affected devices, a successful attack could disconnect remote workers, interrupt access to company systems, and leave IT teams explaining to angry executives why nobody can get anything done.
Picture your CEO demanding an emergency meeting about the outage, only to discover half the team can't connect to the network to join it.
Cisco has released fixes, but companies still need to install them.
If you were responsible for keeping thousands of employees connected, would you be checking your firewall today, or waiting for your CEO to discover the problem before you do?
Polymarket Suspends Trading After Hackers Steal Millions Through Third-Party Software
On October 29, hackers stole about $2.7 million from 726 cryptocurrency wallets on Polymarket, a website where people bet money on real-world events.
The hackers didn't need to break into Polymarket's main systems.
They attacked DebugBear, an outside company that helped Polymarket monitor its website. The hackers secretly added malicious code that ran when customers visited the site.
If you were already logged in, that code could sell your investments and send your money straight to the attackers. You open a website to check your balance, and the website helps someone empty it instead.
That's one expensive way to learn that your money was safer before you logged in.
Polymarket temporarily stopped trading, removed the harmful code, and forced users to log in again.
By November 2, Polymarket had promised $3.9 million in refunds and compensation, including $2.7 million in stolen funds and another $1.2 million for additional losses.
The company said 95% of affected wallets had already received full refunds by October 30.
What happens when your company spends millions protecting its systems, only for a smaller outside vendor to leave the door open? Your security team can have the fanciest tools, the biggest budget, and enough dashboards to decorate an airport control tower.
But if hackers can turn one trusted website tool into a money-stealing machine, how much protection are you really buying?
Please note that this content is for general information only and shouldn't be considered legal, medical, financial, or professional advice. We encourage you to do your own research and consult a qualified professional before making important decisions.